
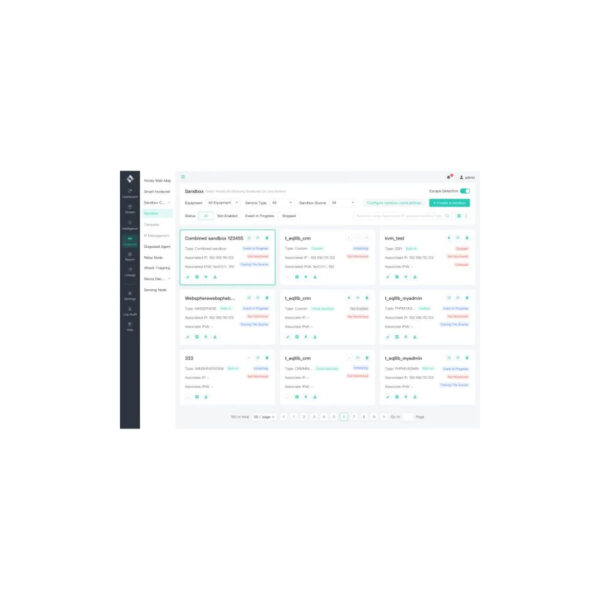
Overview: MoreSec Huanzhen is positioned as an advanced threat hunting and attack tracing system designed for enterprise cybersecurity operations. Based on the available product visuals, it is suitable for organizations that require sandbox-based threat analysis, malware behavior detection, and centralized security investigation support.
Industry: This product is most relevant to cybersecurity, enterprise IT infrastructure, managed security services, finance, government, education, telecom, and data center environments where advanced threat visibility and incident response are important.
Application Scenario: Huanzhen can support SOC teams, network security administrators, and incident response teams in analyzing suspicious files, monitoring sandbox activity, tracing attack behavior, and improving threat investigation workflows.
Product Category: The product fits within cybersecurity platforms, sandbox security systems, threat hunting solutions, and enterprise network defense procurement.
Deployment Environment: The interface suggests centralized management for sandbox resources, making it suitable for enterprise networks, security operation centers, private cloud environments, and data center security zones.
Procurement Purpose: Enterprises may procure MoreSec Huanzhen to strengthen malware analysis capability, improve attack tracing efficiency, support security monitoring workflows, and enhance the overall resilience of IT infrastructure.
Business Value: As part of an enterprise IT hardware and security procurement portfolio, Huanzhen helps connect security technology, IT teams, and operational needs by simplifying sourcing for advanced cyber defense solutions.
